









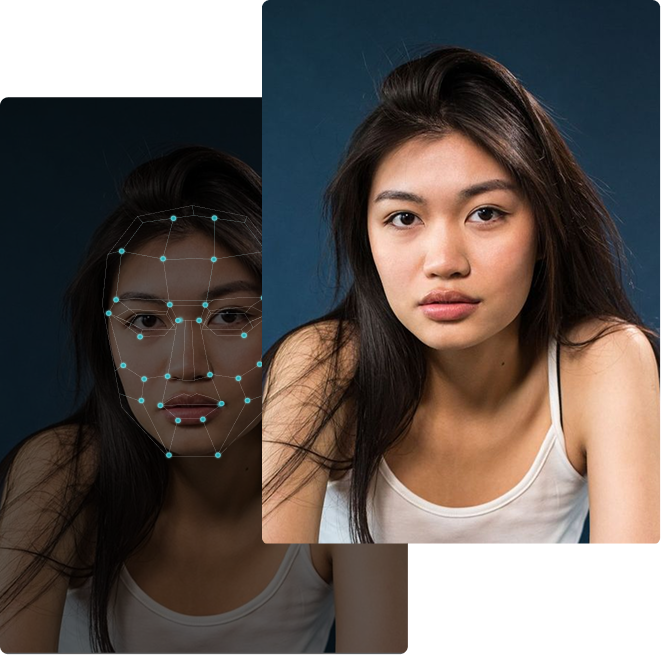


In July 2025, the UK Financial Conduct Authority fined Monzo £21,091,300 for inadequate financial crime systems, after finding that the bank had opened more than 34,000 high-risk accounts in breach of a regulatory restriction. The FCA's central finding was that Monzo's financial crime controls failed to keep pace as its customer base grew almost tenfold. One year earlier, the same regulator fined Starling Bank £28,959,426 for parallel failures in sanctions screening and for repeatedly breaching a requirement not to open accounts for high-risk customers. The pattern is now the template, and in 2026 the dominant delivery mechanism against neobank onboarding is deepfake-driven synthetic identity fraud.
The neobank model that lets a customer open an account in under five minutes also lets a fraud network open hundreds of accounts in an afternoon. 100% digital onboarding, mobile-first SDKs, automated decisioning, and third-party KYC vendor dependency are features that distinguish neobanks from traditional banks on the customer side. They also distinguish neobank onboarding from traditional bank onboarding on the attacker side. Deepfake fraud at a Monzo, Revolut, N26, Chime, or Nubank sized institution is a structurally different problem than deepfake fraud at HSBC or JPMorgan, and the architectural response has to match.
This guide walks through the five deepfake attack vectors that target neobank onboarding specifically, where each one lands in the onboarding pipeline, what regulators now expect, and the detection stack that pushes back. It is written for neobank compliance officers, fraud leads, head of financial crime roles, and product managers at identity verification vendors serving the digital-only banking sector.
- The FCA fined Monzo £21,091,300 in July 2025 after finding the bank opened more than 34,000 high-risk accounts in breach of a regulatory restriction, with its controls failing to keep pace as its customer base grew almost tenfold.
- The FCA fined Starling Bank £28,959,426 in October 2024 for parallel failures in sanctions screening and repeated breaches of a restriction not to open accounts for high-risk customers.
- Fraud-prevention spending at neobanks rose 357%, from $1.8 million to $8 million per institution, with average losses still reaching $2.84 million per institution (PYMNTS, 2026).
- EBA Guidelines EBA/GL/2021/21, updated in October 2023, require liveness detection during remote or digital onboarding when no human agent is present. This is a supervisory expectation enforced through FCA and EBA review, not guidance.
- Neobanks run onboarding SLAs in the single-digit minutes with no branch fallback, which means synthetic identity and deepfake attacks have no in-person check to clear.
- Deepfake selfies routinely defeat simple liveness detection that relies on eye movements and head turns, which is still the baseline control in many neobank onboarding stacks.
- Mule-account farming at neobanks completes the open-to-abandon cycle faster than standard post-onboarding transaction monitoring catches it.
- The 2026 detection posture requires injection-aware liveness, deepfake-specific media classification, mule-portfolio analytics, and tighter integration between onboarding and transaction monitoring.
What Makes Neobank Onboarding Structurally Different?
Neobank onboarding differs from traditional bank account opening in five ways that each amplify the deepfake threat.
The first is that there is no physical branch anywhere in the flow. Chime, Revolut, N26, Monzo, Nubank, SoFi, Starling, and the broader challenger and neobank category have built operating models with no in-person KYC fallback. Every customer the bank onboards comes through the mobile app or web portal, which means every KYC decision is made on digital evidence alone. The option that exists in a traditional bank (direct the applicant to a branch, ask them to come in with their passport) is architecturally not available.
The second is onboarding velocity. The 2026 neobank guide at Crassula identifies the shared operating pattern across the leaders: "They run a single ledger, onboard in under five minutes, and settle most operations without a human in the loop." Sub-five-minute onboarding is a competitive requirement, not an aspiration. The business model depends on converting app install into funded account before the applicant drops off, which concentrates all KYC decisioning into an automated, remote, biometric-only flow.
The third is mobile-first capture. The onboarding SDK runs on the applicant's phone. The camera is the applicant's camera. The document scan is a photo taken through the applicant's device. This is architecturally identical to the setup that camera injection attacks target at crypto exchanges, which we covered in how deepfakes bypass crypto exchange onboarding. The attack surface class transfers directly.
The fourth is the third-party KYC vendor dependency. Onfido, Sumsub, Jumio, Veriff, Persona, and iProov collectively handle the KYC decision for the overwhelming majority of neobank applications in 2026. The vendor's detection quality effectively is the neobank's deepfake defense, which creates a structural single point of failure if the vendor's models have not been updated against the current generation of deepfake tooling.
The fifth is the growth-versus-friction tension. Neobanks compete on frictionless onboarding; every additional verification step is a drop-off cost. The FCA's Monzo decision found that controls failed to keep pace with growth; the implied compliance lesson is that onboarding controls have to scale with customer intake, but the business pressure pushes the opposite direction. The architecturally difficult question is not "what control catches deepfakes" but "what control catches deepfakes without materially increasing drop-off."
Why Neobanks Became Prime Deepfake Targets
Three attacker-side economics make neobanks specifically attractive compared with traditional banks.
The mule-account window is the first and largest. The Sanction Scanner 2026 analysis identified the pattern directly: "Fraudsters open neobank accounts (mule accounts) to receive fraud proceeds then move rapidly to second-hop accounts or crypto and abandon the account within days. The neobank onboarding model that allows legitimate customers to open accounts in minutes also allows mule accounts to open in minutes, and the mule cycle typically completes faster than the monitoring cadence catches it." The speed that defines the customer experience also defines the mule cycle time.
The second is automated decisioning. A traditional bank with manual KYC review has a human analyst who can notice that something is off about an application: a document that matches the template but looks subtly wrong, a selfie that seems to lack natural reaction time, a cluster of applications with similar metadata. A fully automated neobank pipeline has no such pattern-matcher in the loop unless one is explicitly built. A synthetic identity that passes the automated checks passes full stop.
The third is the enforcement target. The FCA's Monzo decision of July 2025 established that neobank compliance failures are now a priority for regulators, with the £21.1 million fine and the finding that 34,000+ high-risk accounts were opened in breach of restrictions. The FCA's Starling decision of October 2024 established the same for sanctions screening failures. EBA review processes across the EU operate under EBA/GL/2021/21, which specifically addresses remote onboarding liveness. From an attacker's perspective, every one of these enforcement actions is a public specification of what controls the target bank is likely to be under-equipped on.
The PYMNTS 2026 data makes the aggregate economics concrete. Fraud-prevention spending at neobanks, digital-only banks, and fintechs rose 357%, from $1.8 million to $8 million per institution. Average losses still reached $2.84 million per institution. The fraud-loss rate dropped 20% (from 0.90 to 0.72 basis points), which indicates that the increased spending is working at the margin, but the absolute loss number remains substantial. The attack has not been solved; it has been partially mitigated at considerable operational cost.
The Five Deepfake Attack Vectors Against Neobank Onboarding
1. Deepfake Selfie Against Basic Liveness
The volume attack is a deepfake selfie submitted against the primary KYC vendor's liveness check. The Sanction Scanner analysis is explicit: "Deepfake selfies beat simple liveness detection that relies on eye movements and head turns." The eye-movement and head-turn active liveness checks that were deployed through 2020-2023 are now the baseline control at many neobanks, and the baseline control no longer holds against consumer face-swap tools.
The attack works because the primary KYC vendor's ISO/IEC 30107-3 presentation attack detection was designed for photos, screen replays, and basic masks (the attacks that defined presentation attack testing when the standard was written). AI-generated selfies produced by 2024-or-later generators are a different attack class, and PAD certification does not automatically cover them. For neobanks whose primary vendor has not refreshed detection models against recent generators, the gap is active.
2. Synthetic Identity Document Plus AI Face
The attack chain that most frequently clears neobank KYC in production is a synthetic identity: a fabricated persona with an AI-generated face, submitted with a matching AI-generated identity document. The document is generated to look like a valid issuing authority's layout (passport, national ID, driver's licence), with internally consistent numbers and a portrait that matches the selfie.
The economics work because AI-generated identity documents sell from around $15 each in bulk on Sumsub-tracked marketplaces, and the mule-account resale value or direct-use value of a verified neobank account substantially exceeds the production cost. This is the same attack architecture we covered in the five vectors fraudsters use to bypass KYC; the difference at a neobank is the volume at which the attack is run.
The FCA's Monzo finding that 34,000+ high-risk accounts were opened in breach of restrictions is a public measure of what synthetic identity volume looks like at scale.
3. Mobile Camera Injection
Camera injection is the delivery layer that lets synthetic video bypass the KYC SDK entirely. The attacker installs a virtual camera driver on an Android device or runs the neobank's app in an emulator with full control of the camera input. When the app requests camera access, it receives a pre-prepared synthetic stream that matches the specific angles and prompts the SDK will request.
MIT Technology Review's April 2026 investigation documented 22 public Telegram channels openly selling virtual camera injectors, deepfake generators, and camera hooking modules from around $30, with several listings advertising specific named banks as reliably bypassable. Sumsub, cited in the same reporting, observed a 180% year-over-year rise in sophisticated multi-step fraud attempts including virtual-camera bypasses.
For neobanks, the architectural problem is that the mobile SDK typically treats the camera stream as trusted input. Injection attack detection, which verifies that the stream originated from a physical camera on a real device, is still an optional module at most tier-one KYC vendors. For a neobank onboarding thousands of accounts per day, it should be a procurement baseline rather than an option.
4. Mule Account Farming at Volume
The mule-account farm attack industrialises the three vectors above. A single operator uses automated tooling to onboard dozens or hundreds of neobank accounts in a short window, each with a distinct synthetic identity and deepfake biometric chain. The accounts are not used by the operator; they are activated as mules to receive fraud proceeds from other crimes (scams, phishing, authorized push payment fraud, pig butchering).
Sumsub's 311% spike in synthetic identity document fraud in North America in Q1 2025 compared with Q1 2024, and the 180% year-over-year rise in multi-step fraud, are direct measurements of this pattern. The neobank economic exposure is twofold: the direct fraud loss from mule activity, and the AML enforcement exposure from having onboarded the mule accounts in the first place. The FCA's Monzo and Starling decisions make the second exposure concrete.
At portfolio level, mule farms produce distinctive signals that individual-account checks miss: co-located registration (shared IP ranges, shared device characteristics), co-timed registration patterns, consistent onboarding paths (same questions answered in similar sequence), and co-ordinated first-funding patterns. The detection problem is not "is this account suspicious" but "do these 40 accounts form a coordinated farm."
5. Account Takeover Via Video KYC Step-Up
Some neobanks run video KYC step-ups for high-tier accounts, suspicious activity reviews, or recovery scenarios. For these flows, the attack of choice is real-time face swap. The attacker drives the video call themselves but runs a consumer face-swap model that replaces their face, frame by frame, with the target customer's face (sourced from social media or a prior data breach).
The attack path mirrors the one we documented in how fraudsters bypass crypto exchange onboarding for the MEXC case. Active challenges (turn your head, cover part of your face, read a number) fail against modern real-time face-swap because the attacker's motion drives the swap. For neobanks, this surface typically appears at recovery or step-up rather than initial onboarding, but the attack pattern is identical.
Where Attacks Land in the Neobank Onboarding Pipeline
The seven-stage onboarding pipeline that Shufti and others identify as standard across neobank operators (data collection, document capture, document authentication, biometric match, liveness, risk scoring, decision) is where the attack surface actually lives. Understanding which attack lands where decides where control investment matters.
At document authentication, the dominant attack is the synthetic identity document. The control that catches it is authentication beyond template matching: microprint and watermark inspection at image resolution, consistency checks between document portrait and selfie across multiple signals, and NFC chip verification for eMRTD passports and modern eIDs where supported.
At biometric match and liveness, the dominant attack is the AI-generated selfie or face-swap video, delivered via camera or via injection. The controls that catch it are injection attack detection at capture, dedicated deepfake media classification running alongside the primary vendor's liveness, and physiological signal detection.
At risk scoring, the dominant attack is the account that has cleared the visible checks and now needs behavioural or device-level flags to catch. The controls are device fingerprinting, behavioural biometrics during session (typing cadence, mouse movement, session timing), and portfolio-level pattern matching against known mule-farm signatures.
At the post-onboarding transaction monitoring boundary, the dominant attack is the mule account activating within the monitoring lag window. The control is tighter integration between onboarding risk scores and transaction monitoring thresholds, so that a borderline onboarding score tightens monitoring on first transactions rather than being discarded at the point of account activation.
The Regulatory Picture: What Regulators Expect
The regulatory environment around neobank onboarding has sharpened substantially through 2024-2026, and deepfake controls are now specifically scoped.
EBA/GL/2021/21, the European Banking Authority's guidelines on remote customer onboarding solutions updated in October 2023, require liveness detection during remote or digital onboarding when no human agent is present. The CheckFile.ai 2026 analysis is direct about the enforcement posture: "This is not guidance, it is a supervisory expectation enforced through FCA and EBA review processes. Liveness detection must confirm that the person presenting the document is physically present, not a photograph, video replay, or deepfake."
The FCA's enforcement record is the practical specification of what compliance looks like in the UK. The Monzo £21,091,300 fine (July 2025) specifically cited failure of financial crime controls to keep pace with customer growth and the opening of 34,000+ high-risk accounts in breach of a restriction. The Starling Bank £28,959,426 fine (October 2024) specifically cited sanctions screening failures and repeated breaches of a restriction not to open accounts for high-risk customers. Both decisions established that neobank growth plus inadequate control scaling plus demonstrable failure to meet the restriction equals material penalty.
In the EU, BaFin's regulatory scrutiny of N26 through 2023-2024 followed the same pattern: growth acceleration plus KYC control gaps plus supervisory restriction on onboarding pace. In the US, FinCEN proposed revisions to the Bank Secrecy Act AML programme requirements on April 7, 2026, which explicitly address AI-generated identity documents and biometric deepfakes as covered risks.
The practical consequence for any neobank compliance officer evaluating deepfake controls in 2026 is that the supervisory question is no longer "are you using liveness" but "is your liveness capable of catching the deepfake and injection attacks that are now standard in the attacker toolkit." The regulatory posture has moved from compliance with a baseline to demonstration of control against a specifically-named threat class.
How to Detect and Stop Deepfake Onboarding at Neobanks
A resilient 2026 neobank onboarding stack runs five detection families in parallel, with the primary KYC vendor treated as one input to a layered decision rather than the whole decision.
Document authentication beyond template matching catches AI-generated identity documents at the first check. The baseline is to combine template matching with microprint and watermark inspection, document-to-selfie consistency across multiple signals (not just a face match score), and NFC chip verification for eMRTD passports and modern eIDs. This layer closes the volume vector described in attack pattern 2.
Modernised liveness with deepfake-specific detection addresses the AI selfie attack. The baseline liveness check (head turn, eye movement) is now a legacy control; the current baseline is passive liveness combined with dedicated deepfake media classification that has been updated against generators released in the last 90 days. The Sanction Scanner observation that "deepfake selfies beat simple liveness detection that relies on eye movements and head turns" is the current state, and the gap is addressed by a different control family, not by stronger head-turn prompts.
Injection attack detection at capture addresses the camera injection vector directly. The MIT-documented attack infrastructure is overwhelmingly injection-based, and primary KYC vendor liveness certification does not cover injection. The control verifies that the capture stream originated from a physical camera on a real device. For neobanks, this is now a procurement baseline alongside the primary KYC vendor's standard offering.
Portfolio-level fraud analytics catches the mule-farm attack at the pattern level. Shared IP ranges, device characteristics, onboarding path similarity, and co-timed registration patterns are the signals. Most neobanks that are investing in fraud detection are investing at the individual-account level; the portfolio-level view is where the farms become visible, and where the FCA-pattern enforcement risk concentrates.
Onboarding-to-transaction-monitoring integration closes the mule-cycle window. The attack economics documented by Sanction Scanner depend on the mule cycle completing before monitoring catches it. Tightening monitoring thresholds for accounts that scored borderline at onboarding closes the window without materially affecting the customer experience for clean onboardings. This is the architectural shift that most meaningfully addresses the mule-account AML exposure that drives the FCA enforcement.
DuckDuckGoose publishes deepfake detection accuracy against generators the detection system has not been trained on, which matters directly for neobank onboarding where the next generator a mule-farm operator uses will not be the one in the primary KYC vendor's training set.
Common Mistakes
Three mistakes recur in neobank fraud and compliance programs that have otherwise invested seriously in KYC.
Treating the primary KYC vendor as the entire deepfake defense. Onfido, Sumsub, Jumio, Veriff, Persona, and iProov are strong platforms, but the industry consensus through 2026 is that certified liveness alone does not cover injection attacks or AI-generated media from recent generators. The architectural shift is to treat the primary vendor as one layer in a five-layer stack.
Optimising onboarding exclusively for drop-off rather than fraud outcome. Neobank product and growth teams correctly focus on onboarding completion rates; neobank fraud and compliance teams correctly focus on fraud outcomes. The structural problem is that these teams often optimise on separate metrics, and the controls that materially reduce deepfake fraud (injection attack detection, portfolio-level analytics) do not visibly affect drop-off because they run in parallel with the primary flow. Framing fraud controls as drop-off neutral is a prerequisite for the investment conversation to go anywhere.
Under-investing in the onboarding-to-monitoring handoff. The FCA's Monzo decision specifically cited controls that failed to keep pace with growth. In practice, many of the controls that pass regulatory review focus on onboarding or on transaction monitoring, but not on the handoff between them. The mule cycle that defines the real exposure lives in the handoff, and the handoff is typically under-instrumented.
Practical Recommendations
A pragmatic 2026 roadmap for neobank compliance has four priorities.
Add injection attack detection to the mobile onboarding SDK. The MIT Technology Review investigation makes this concrete: the specific attack infrastructure now commercially available targets exactly the capture layer that most KYC vendors do not independently attest. If your current vendor stack has no explicit injection attack detection control, assume your onboarding is exposed to the dominant 2026 attack class.
Layer a dedicated deepfake detector alongside the primary KYC vendor. The two model classes are not substitutes. A detector that reports performance against generators it has not seen in training is the right vendor evaluation metric for a workload where the next attack will not use the generator that was dominant three months ago.
Stand up portfolio-level fraud analytics. Account farms are detectable at the portfolio level in ways that no individual account check can match. For a neobank, the FCA-style enforcement risk is specifically concentrated at the volume end of synthetic identity fraud, which makes portfolio-level analytics not just a fraud control but a compliance control.
Tighten the onboarding-to-monitoring handoff. Borderline onboarding scores should translate into tighter transaction monitoring thresholds, not be discarded at the point of account activation. This is the architectural shift that closes the mule cycle window that drives the practical AML exposure.
DuckDuckGoose's DeepDetector is designed specifically for the detection layer in this stack, with model performance tested against generators the detection system has not been trained on, which addresses the generalisation gap that defines the 2026 neobank onboarding threat.
Frequently Asked Questions
Why are neobanks specifically targeted by deepfake onboarding fraud?
Three structural features converge. Neobanks run 100% digital onboarding with no branch fallback, so there is no in-person KYC step to clear. They run sub-five-minute onboarding SLAs with automated decisioning, so synthetic identities with deepfake biometrics have no human analyst in the loop to notice irregularities. And they operate at scale (Monzo 12M+, Revolut 65M+, Nubank 100M+), which means thousands of applications per day, which gives mule-account farming the volume cover it needs.
What did the Monzo FCA fine actually find?
The FCA fined Monzo £21,091,300 in July 2025 for inadequate financial crime systems between October 2018 and August 2020, and for repeatedly breaching a later restriction by opening more than 34,000 high-risk accounts. The central finding was that Monzo's financial crime controls failed to keep pace as its customer base grew almost tenfold. Some accounts were opened with addresses listed as well-known London landmarks, which the controls failed to flag.
What does EBA/GL/2021/21 require?
EBA Guidelines EBA/GL/2021/21, updated in October 2023, require liveness detection during remote or digital onboarding when no human agent is present. The CheckFile.ai 2026 compliance analysis is direct that this is a supervisory expectation enforced through FCA and EBA review, not voluntary guidance. Liveness detection must confirm the person is physically present, not a photograph, video replay, or deepfake.
Does ISO/IEC 30107-3 liveness certification cover modern deepfakes?
Partially. ISO/IEC 30107-3 covers presentation attack detection, which addresses deepfakes shown to a physical camera. It does not cover injection attacks, which are the dominant 2026 delivery method per MIT Technology Review's investigation. It also does not measure performance against AI-generated media that the certified system has not been trained on. Treat the certification as necessary but not sufficient.
What is a mule account farm and why are neobanks specifically exposed?
A mule account farm is the attacker pattern of opening dozens or hundreds of accounts in a short window, each with a distinct synthetic identity, for use as mule accounts to receive fraud proceeds. Neobanks are specifically exposed because the open-to-abandon cycle completes faster than standard post-onboarding transaction monitoring catches it. The onboarding speed that defines the customer experience also defines the mule cycle speed.
How much are neobanks actually spending on fraud prevention in 2026?
PYMNTS 2026 reporting found fraud-prevention spending at neobanks and digital-only fintechs rose 357%, from $1.8 million to $8 million per institution. Average losses still reached $2.84 million per institution, though the fraud-loss rate dropped 20% (from 0.90 to 0.72 basis points). The absolute loss number remains substantial, and the spending increase is working at the margin rather than closing the gap entirely.
How should a neobank compliance officer evaluate a deepfake detection vendor?
Ask for test results against three independent categories: ISO/IEC 30107-3 presentation attacks, injection attack scenarios (virtual camera, emulator, API hook), and AI-generated media from generators the vendor has not explicitly trained on. Confirm the model refresh cadence (monthly updates are the 2026 baseline) and request generalisation scores against unseen generators. The vendor's integration pathway alongside the existing primary KYC stack is as important as the detection accuracy itself.
What is the single highest-leverage control shift for a neobank in 2026?
Add injection attack detection to the mobile onboarding SDK. The commercial attack infrastructure now targeting neobanks is overwhelmingly injection-based per MIT Technology Review, and primary KYC vendor liveness certification does not cover injection. Combined with portfolio-level fraud analytics (which addresses the mule-farm volume problem and the FCA-pattern enforcement risk), this is where most of the structural gap closes.
About the author