









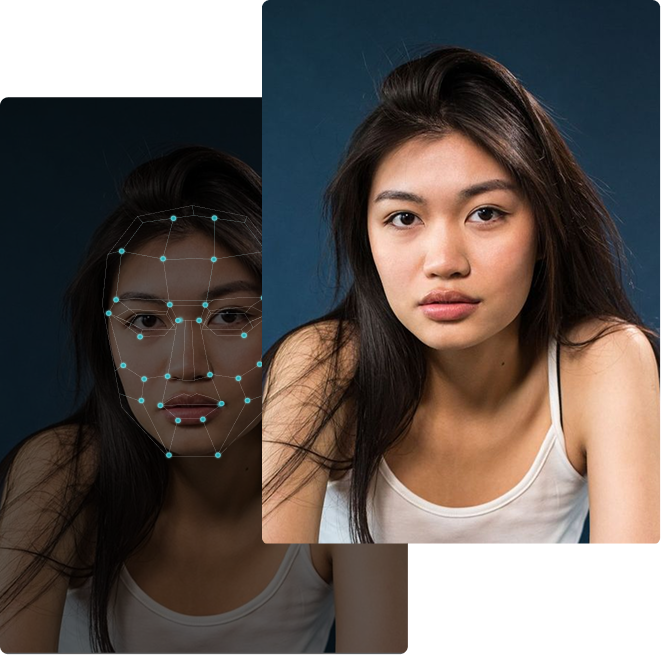


Deepfake wire fraud at nine-figure scale is now a documented pattern, and correspondent banking is the delivery mechanism that carries the money to its destination. On November 6, 2026, federal prosecutors in the Southern District of New York unsealed an indictment against three men (Jacob Soall, Sharon Hazan, and Guy Sheetrit) alleging a $129 million AI-enabled executive impersonation fraud scheme that ran from July 2024 to February 2026. According to the DOJ, the men used AI to clone the voices and images of real CEOs and lawyers at international law firms, then targeted accounting staff with wire-transfer authority at victim companies around the world. The resulting wires were sent to accounts in the United States, Spain, Portugal, Greece, the UAE, Singapore, Austria, Slovakia, and China. The DOJ announced its Super Intelligence Task Force on the same day as the indictment.
The $129 million did not get to nine countries by itself. It moved through correspondent banking. Every one of those international wires cleared through at least one correspondent bank, and in most cases through two or three, operating in a payment chain where no one bank had direct visibility into the deepfake deception that initiated the transfer. Correspondent banking is where every downstream deepfake attack on a corporate customer or a smaller bank eventually arrives. It is also where the attacks that specifically target correspondent banking itself (RFI response spoofing, compliance officer impersonation, trade finance confirmation deepfakes) now operate.
This guide walks through how deepfake fraud actually reaches correspondent banking, the five attack vectors operating in production right now, the UCC Article 4A liability picture that determines who bears the loss, and the detection stack correspondent banks are building. It is written for correspondent banking relationship managers, financial crime compliance officers at correspondent and respondent banks, treasury operations leads, and product managers at the wire-transfer and AML systems serving the sector.
- DOJ unsealed an indictment on November 6, 2026 charging three men with a $129 million AI-enabled executive impersonation fraud scheme, with wires routed to nine countries through correspondent banking channels.
- At least one case in the indictment saw a New York-area bank's back office catch a $2.85 million wire before it left, after an employee had already authorised it, per CCG Catalyst's November 18 analysis.
- The Hong Kong Arup case (2024) saw a bank manager authorize approximately $25.6 million in transfers after a multi-person deepfake video conference where all other participants were AI-generated executives.
- The 2026 Trustmi fraud resilience report found impersonation fraud rose from 35% to 40% year-over-year, with wire transfers reclaiming the top spot as the most-targeted payment type for business email compromise.
- 6% of finance teams reported direct deepfake audio fraud and 6% reported deepfake video fraud in 2026 surveys, with 45% experiencing broader business email compromise.
- UCC Article 4A creates a specific liability picture where wires initiated by a deceived-but-authorized person may still be effective as the customer's order, leaving the customer rather than the bank with the loss.
- FATF Recommendation 13 and the Wolfsberg CBDDQ require correspondent banks to assess the AML and financial crime controls of their respondent banks, which is now a specific channel for deepfake-polluted KYC data to enter the correspondent pipeline.
- The highest-leverage control shift is adding deepfake-aware voice and video authentication at the executive authorization moments where the attack lands, rather than relying on transaction monitoring to catch the wire after it is in flight.
What Is Correspondent Banking and Why Does It Matter Here?
Correspondent banking is the arrangement where one bank (the correspondent) holds accounts for another bank (the respondent) to facilitate cross-border payments, clearing, trade finance, and foreign exchange. The respondent's customer initiates a payment, the respondent instructs its correspondent via SWIFT, and the correspondent moves the money through its own payment rails to the beneficiary's bank, possibly through further correspondent relationships.
The structure matters for the deepfake threat model in three ways.
First, the correspondent bank typically has no direct relationship with the respondent's underlying customer. The correspondent sees a MT 103 or MT 202 message from a known counterparty, with originator and beneficiary identity information that the respondent has collected and transmitted. The correspondent relies on the respondent's KYC and transaction monitoring, which is formalised in FATF Recommendation 13's requirement to assess the respondent's AML controls and Wolfsberg's Correspondent Banking Due Diligence Questionnaire (CBDDQ).
Second, the chain often spans jurisdictions with inconsistent control standards. The DOJ's $129M indictment lists nine countries as destinations. Each of those destinations sits behind at least one correspondent relationship, and the quality of the detection at each hop is independent. One strong correspondent in a chain of weak respondents is not enough to catch an initiation-stage deepfake.
Third, the economics of correspondent banking have pushed toward de-risking (exiting relationships with higher-risk respondents) rather than deeper controls on the remaining relationships. The Wolfsberg Group's analysis across 2023-2026 has documented the de-risking trend and its downstream effect on financial inclusion. The practical consequence for the deepfake threat model is that the surviving correspondent relationships now carry more volume and more compliance expectation, which is where control investment has to concentrate.
Why Correspondent Banking Is the Terminal Stop for Deepfake Fraud
Deepfake fraud at the executive-impersonation layer is almost never aimed at a correspondent bank directly. It is aimed at a corporate customer of a smaller bank, a mid-cap company with international operations, or a corporate treasury department with wire-transfer authority. The role of correspondent banking in the attack economics is that it is the delivery mechanism.
The DOJ $129M case is the clearest illustration. The victim employees were accountants and finance staff at corporate victims, not at banks. The deepfake was of their own company's CEO, not of a bank officer. The attack path was: deepfake voice or video of the CEO convinces an authorised employee to initiate a wire, the wire goes through the victim company's primary bank, that bank's correspondent relationship clears the wire to a destination country, and the destination bank credits the beneficiary account. The correspondent bank is the pipe that carries the money, not the point of deception.
The same applies to the Arup Hong Kong case (approximately $25.6 million, 2024, multi-person deepfake video conference) and the UAE voice-cloning scam (approximately $35 million, 2020, cloned company director voice directing a bank manager). The initiation happened at the corporate or retail customer layer; the money moved through correspondent banking.
That architecture creates a specific control problem. The correspondent bank has the most sophisticated AML and transaction monitoring infrastructure in the chain, but it has the least context about the originating event. The respondent bank has more context but less specialised fraud detection. The corporate victim has the most context but no transaction monitoring at all. The attack succeeds because the information required to detect it is distributed across parties that do not share it in real time.
That is why FATF Recommendation 13 and the Wolfsberg CBDDQ matter to the deepfake threat model. They are the mechanism by which the correspondent bank acquires some measure of the context it needs: by demanding that the respondent attest to specific controls (customer due diligence, transaction monitoring, politically exposed person screening, sanctions screening). A respondent bank with a mule-account problem, as we covered in how deepfakes target neobank onboarding specifically, produces polluted KYC data that then enters its correspondent's pipeline through every outbound wire.
The Five Deepfake Attack Vectors That Reach Correspondent Banking
1. Downstream CEO Impersonation Driving Wire Transfers
The dominant volume attack is CEO impersonation of a corporate customer. The DOJ $129M indictment is the specific case; business email compromise reporting from the 2026 Trustmi fraud resilience report is the broader pattern. The attacker clones the voice or video of a corporate executive and convinces an authorised employee to initiate a wire transfer, often paired with a secondary deepfake of an outside attorney to add legal plausibility.
The correspondent bank sees a legitimate MT 103 from a known respondent, representing a wire from a known corporate customer, on an account that has been active for years. The detection signal that might catch this is a wire to a new beneficiary in an unusual geography, in a round-number amount, with a reference line that mentions a confidential transaction. Transaction monitoring at the correspondent can flag these patterns, but by the time the alert fires the money has typically already moved through.
The CCG Catalyst November 18, 2026 analysis highlights one bright spot from the indictment: a New York-area bank's back office caught a $2.85 million wire before it left, after an employee had already been deceived and had authorised it. The pattern that caught it is the architecture that works: layered controls where the back office review is a separate check from the authorised initiation.
2. Multi-Person Deepfake Video Conference Authorization
The Hong Kong Arup case is the reference incident: a bank manager was deceived into authorizing approximately $25.6 million in transfers after joining a multi-person video conference where all of the other participants, purporting to be senior business executives, were AI-generated deepfakes. This is the extreme version of the attack: not a single voice clone but a full synthetic environment.
For correspondent banking, the same attack pattern applies to any relationship moment where multiple executives of a respondent bank or corporate customer confer with a correspondent bank's team: large transaction authorization, unusual trade finance arrangement, significant policy change, emergency credit facility use. A deepfake video conference with the respondent's senior team authorising an unusual flow has the same effect as the Arup attack had on the manager in Hong Kong.
3. Direct Correspondent-to-Respondent RFI Response Spoofing
The underdocumented vector is spoofing of Request For Information (RFI) responses. When a correspondent bank's transaction monitoring flags a transaction, the correspondent sends an RFI to the respondent asking for additional information (purpose of payment, beneficial ownership, source of funds). The respondent's compliance officer responds, typically by email with supporting documentation and sometimes by voice or video call for high-value or high-risk flows.
A deepfake of the respondent bank's compliance officer, email account impersonation, or voice call purportedly from the compliance officer responding to an RFI is sufficient to clear a flagged transaction in a high-trust bilateral relationship. The attack pattern is documented across the broader BEC category and transfers directly to this inter-bank communication surface. Direct documented cases specifically targeting correspondent banking RFI processes are not yet public, but the attack class is what compliance teams across tier-one correspondents are now scoping into their 2026 threat models.
4. Trade Finance Confirmation Spoofing
Trade finance (letters of credit, documentary collections, bank guarantees) runs on confirmations between banks. An issuing bank confirms a letter of credit to an advising bank, which confirms to a beneficiary. The confirmations travel via SWIFT MT 700 series messages, supplemented by email and voice communication for clarification and amendment.
Deepfake voice and video of a bank officer at the issuing bank calling the advising bank to request an amendment, confirm a shipping document, or authorise a drawing is a documented emerging attack pattern across the 2026 trade finance fraud reporting. The attack sits at the intersection of correspondent banking and trade finance and inherits the limitations of both: bilateral trust, operational complexity, and limited time budgets for verification.
5. Compliance Officer Impersonation for KYC Data Requests
The slower-cycle attack is compliance officer impersonation during the Wolfsberg CBDDQ or FATF Recommendation 13 due diligence process. A correspondent bank onboarding a new respondent, or periodically re-reviewing an existing respondent, collects detailed information about the respondent's AML controls, customer due diligence procedures, politically exposed person screening, and sanctions programme.
A deepfake of a respondent bank's senior compliance officer, either during the initial due diligence interview or during a follow-up clarification, produces polluted CBDDQ data that then becomes the correspondent's basis for accepting the relationship. The polluted data persists for the life of the relationship, which can be years, and contaminates every subsequent decision the correspondent makes about that respondent.
How Fraud Flows Through the Correspondent Pipeline
Understanding where the deepfake attack lands and where control investment matters requires tracing the pipeline from initiation to settlement.
Initiation at the respondent bank is where the deepfake deception usually happens. A corporate customer's employee is deceived, the respondent bank receives a wire instruction from the authorised corporate account, and the respondent processes it through standard controls. The respondent's transaction monitoring may flag the wire based on amount, destination, or beneficiary; it does not catch the fact that the initiation was deepfake-driven.
SWIFT message transmission is the handoff. The respondent sends an MT 103 (customer credit transfer) or MT 202 (bank-to-bank credit transfer, often used for cover payments). The message carries structured information about originator, beneficiary, amount, currency, and reference. The correspondent receives this and has no visibility into the authorisation chain at the corporate victim.
Correspondent processing runs the correspondent's own transaction monitoring, sanctions screening, and risk scoring. If the correspondent's models catch the pattern (unusual beneficiary, amount, geography, reference, timing), the wire can be held for review and an RFI sent to the respondent. This is the stage where the CCG Catalyst-cited $2.85 million interception occurred: layered back-office review caught what the front-office authorisation did not.
Nostro reconciliation is the settlement stage. Funds move through the correspondent's nostro account at the beneficiary's bank's correspondent, or through further correspondent hops. Once reconciled, the wire is substantively unrecoverable without the cooperation of the receiving bank and sometimes of local law enforcement in the beneficiary's jurisdiction.
Recovery attempt is the back-end reality. The DOJ $129M indictment destinations (nine countries including Spain, Portugal, Greece, UAE, Singapore, Austria, Slovakia, and China) illustrate why recovery is structurally slow. Each jurisdiction has different mutual legal assistance procedures, different civil recovery mechanisms, and different cooperation timelines. By the time recovery is attempted, the funds have typically been through multiple accounts and converted to assets or to other currencies.
The UCC Article 4A Liability Problem
For US correspondent banking, UCC Article 4A is the framework that determines who bears the loss when a deepfake-induced wire goes wrong. The Wright Law Firm's April 2026 analysis is the clearest public treatment.
Article 4A operates on a two-part test. First, was the payment order effective as the customer's order? If the order was initiated by an authorised person using the agreed authentication procedure, the order is effective and the customer is bound by it, even if the authorised person was deceived. Second, if the order was not actually authorised by the customer, was the bank's security procedure commercially reasonable? If yes, the bank can shift the loss to the customer under Section 4A-202.
Deepfake wire fraud falls uncomfortably in the gap between these categories. The transfer is initiated by an authorised person who was deceived, which arguably satisfies the first test and makes the customer bear the loss. But the authorisation was the product of fraud, which creates the question of whether the bank's security procedure should have caught the deception.
The Wright Law analysis notes that as of April 15, 2026, the firm could not confirm any published appellate case applying Article 4A to a deepfake-initiated wire. The legal picture is therefore underdeveloped, and the practical consequence is that corporate victims are typically absorbing the loss in uncontested cases, while any contested case is likely to produce the first appellate precedent in this area over 2026-2027.
Insurance coverage is a parallel problem. Social engineering, computer fraud, and funds-transfer-fraud coverage categories often turn on policy-specific wording. Deepfake wire fraud is AI-enabled but human-initiated, which puts it in the grey zone across most policy categories. The practical consequence is that insurance recovery is contested in many documented cases, and corporate treasuries that have not specifically addressed deepfake coverage with their broker are typically underinsured against this exposure.
How Correspondent Banks Can Detect and Stop This
A resilient 2026 correspondent banking posture against deepfake fraud operates across five control families, each addressing a distinct point in the pipeline.
Transaction monitoring at the correspondent remains the baseline. Pattern-based models that catch unusual beneficiaries, new destinations, round-number amounts, and reference lines mentioning confidential transactions are the controls that caught the $2.85 million New York case. These models are generally mature at tier-one correspondents; the opportunity is to tune for the specific signatures of deepfake-initiated wires (first-time beneficiary in a jurisdiction, no prior commercial history between the parties, time pressure communicated in the reference) rather than relying on generic AML patterns.
Deepfake-aware voice and video authentication at executive authorisation moments is the control that addresses the initiation layer. For correspondent-to-respondent communications specifically, voice deepfake detection running on RFI response calls and trade finance confirmation calls catches the vector described in attack patterns 3 and 4. The infrastructure is now commercially available; the integration challenge is operational (running detection on voice-channel communications without materially slowing the response cycle).
Enhanced KYC data quality scoring on respondent due diligence addresses the CBDDQ pollution vector. The correspondent's assessment of a respondent's AML controls should include specific scoping of the respondent's deepfake defenses at onboarding, in RFI response processes, and in the compliance officer identification used during due diligence interviews. This is an extension of existing CBDDQ rather than a replacement, but the specific questions the industry is converging on through 2026 have not yet reached a uniform standard.
Back-office layered review at the correspondent is the control that caught the New York bank's $2.85 million. Front-office authorisation plus back-office review, with review triggered by risk signals, is a layered posture that catches what either layer alone would miss. The operational economics work because only a small percentage of wires trigger the back-office path; the ones that do are the ones where the architectural redundancy pays off.
Cross-correspondent intelligence sharing closes the pipeline-level gap. Industry forums including the Wolfsberg Group and the regional correspondent banking councils are actively building intelligence-sharing infrastructure specifically for deepfake-driven wire fraud. The 2026 posture is informal but moving toward formal: wallet-level sharing, beneficiary-pattern sharing, and incident-notification protocols that allow correspondent banks to warn each other when a specific deepfake-driven pattern is detected.
DuckDuckGoose publishes deepfake detection accuracy against generators the detection system has not been trained on, which matters directly for the voice and video authentication layer at correspondent-to-respondent communications, where the attacker's generator will not be the one in the detection vendor's training set.
Common Mistakes
Three mistakes recur in correspondent banking fraud and compliance programs that have otherwise invested seriously in AML.
Treating transaction monitoring as the primary deepfake control. Transaction monitoring runs after the wire is initiated and sometimes after the money is in flight. It catches patterns but does not stop deception at initiation. The CCG Catalyst framing is direct: "The CEO's voice is not a payment control." The control gap is at the authorisation moment, not at the transaction-monitoring moment, and the appropriate control is authentication of the human initiating the wire rather than scoring of the wire after the fact.
Relying on respondent attestation without verifying the control substance. The Wolfsberg CBDDQ and FATF Recommendation 13 require the respondent to attest to its controls. Attestation is a necessary but weak signal; the correspondent's own assessment of the substance of the respondent's controls (including through pilot incident reviews, test cases, and targeted follow-up on reported fraud) is what actually calibrates the risk. Correspondent banks that treat the CBDDQ response as sufficient are structurally exposed to the CBDDQ pollution vector described above.
Under-investing in voice and video channel deepfake defenses because these feel like corporate customer problems rather than bank problems. The RFI response and trade finance confirmation vectors are specifically bank-to-bank attack surfaces, not corporate customer problems. Correspondent banks that scope deepfake defense only around their corporate customer base miss the direct bilateral attack vector.
Practical Recommendations
A pragmatic 2026 roadmap for correspondent banking fraud teams has four priorities.
Add deepfake-aware voice and video authentication at RFI response and trade finance confirmation channels. The MIT Technology Review documentation of the commercial deepfake infrastructure makes this concrete: the tooling attackers need to impersonate a respondent bank's compliance officer in a voice call now costs tens to hundreds of dollars. The defense requires equivalent tooling on the correspondent side, running on the specific voice and video channels where the bilateral communication happens.
Extend CBDDQ scoping to specifically address deepfake controls at respondents. The CBDDQ was designed for a 2010s-era control landscape. The 2026 extension is specific questions about the respondent's onboarding deepfake defenses, compliance officer identity authentication, and incident response for deepfake-driven wire fraud. The correspondent's basis for accepting the relationship becomes defensible only if these questions are asked and the answers are verified in substance.
Build back-office layered review for wires that trigger specific risk signals. The $2.85 million New York bank interception demonstrates the architecture. Front-office authorisation plus back-office review, with review triggered by first-time beneficiary in a new jurisdiction, round-number amount, or time-pressure framing, catches the attacks that the front-office alone cannot catch.
Formalise cross-correspondent intelligence sharing on deepfake incidents. The industry is already moving in this direction informally; the formal infrastructure (incident notification protocols, pattern-sharing APIs, shared watchlists for beneficiary accounts linked to deepfake-driven wire fraud) is where the 2026-2027 investment is landing. Correspondent banks that are early participants gain earlier visibility into emerging attack patterns.
DuckDuckGoose's DeepDetector is designed specifically for the voice and video detection layer in this stack, with model performance tested against generators the detection system has not been trained on, which addresses the generalisation gap at the exact communication channels where deepfake fraud enters the correspondent pipeline.
Frequently Asked Questions
How does a deepfake attack on a corporate customer actually reach a correspondent bank?
The deepfake deception happens at the corporate customer, who authorises a wire that their primary bank processes. The primary bank sends the wire via SWIFT to its correspondent, which clears it to the destination country. The correspondent bank sees a legitimate-looking wire from a known respondent with documented originator information; it has no visibility into the deepfake event that initiated the transfer. In the DOJ $129M case, the wires reached nine countries via correspondent banking channels.
What did the DOJ $129M indictment actually allege?
On November 6, 2026, federal prosecutors in SDNY charged three men with wire fraud, aggravated identity theft, and money laundering conspiracy for an AI-enabled executive impersonation scheme that ran from July 2024 to February 2026. The defendants allegedly used AI to clone the voices and images of CEOs and lawyers, then targeted accounting staff with wire-transfer authority at victim companies. Wires went to the US, Spain, Portugal, Greece, UAE, Singapore, Austria, Slovakia, and China. The DOJ announced its Super Intelligence Task Force on the same day.
What is UCC Article 4A and how does it apply to deepfake wire fraud?
UCC Article 4A is the US legal framework for wire transfer liability. It operates on a two-part test: whether the payment order was effective as the customer's order, and if not, whether the bank's security procedure was commercially reasonable. Deepfake wire fraud sits uncomfortably in the gap: the order was initiated by an authorised person who was deceived, which may satisfy the first test and leave the customer with the loss. No published appellate case has addressed this specifically as of April 2026, so the legal picture is still developing.
How does the Wolfsberg CBDDQ relate to deepfake risk?
The CBDDQ is the Wolfsberg Group's standard questionnaire that correspondent banks use to assess the AML and financial crime controls of respondent banks. In the deepfake threat model, the CBDDQ process is itself a potential attack surface: a deepfake of a respondent bank's compliance officer during the due diligence interview can produce polluted attestation data. Beyond that, the questionnaire's scope for assessing a respondent's deepfake defenses is still evolving, and 2026-era CBDDQs are moving toward specific scoping of these controls.
What was the Hong Kong Arup case and why is it the reference incident?
In 2024, a bank manager at Arup Hong Kong was deceived into authorising approximately $25.6 million in transfers after joining a multi-person video conference where all of the other participants, purporting to be senior business executives, were AI-generated deepfakes. It is the reference incident because it is the first widely-documented case of multiple deepfakes in a live business meeting used to execute a fraud at this scale.
Can a correspondent bank detect a deepfake-initiated wire after it has been authorised?
Sometimes. Transaction monitoring at the correspondent can flag the specific patterns associated with deepfake-driven wires (unusual beneficiaries, new destinations, round-number amounts, reference-line indicators), and layered back-office review can catch wires after front-office authorisation. The CCG Catalyst November 2026 analysis highlights one bank case where back-office review caught a $2.85 million wire after an employee had authorised it. The economics depend on catching the wire before nostro reconciliation, after which recovery becomes structurally difficult.
What is the single highest-leverage control shift for correspondent banking in 2026?
Add deepfake-aware voice and video authentication at the bank-to-bank communication channels where deception lands: RFI response calls, trade finance confirmation calls, and large-transaction authorisation calls with respondent counterparts. Transaction monitoring alone runs after the wire is in flight; the appropriate control is at the human authorisation moment, and the technology to run deepfake detection on voice and video channels is now commercially available.
How should a correspondent bank evaluate a deepfake detection vendor?
Ask for test results against three categories: voice deepfake detection against 2026 voice-cloning tools, video deepfake detection against 2026 video generators (Sora 2, Veo 3.1, Kling 3.0 class), and generalisation performance against generators the vendor has not explicitly trained on. Confirm the model refresh cadence (monthly updates are the 2026 baseline given how fast generation tooling evolves). The integration pathway into the specific voice and video channels in the correspondent's operational flow is as important as the detection accuracy itself.
About the author