









Presentation attacks and injection attacks are the two ways an attacker gets a fake face past a verification system, and they are frequently confused, including by vendors. The confusion matters, because the two are defeated by completely different technology, and a defense against one does nothing against the other. The distinction comes down to a single question: where does the fake enter the system?
This piece explains how presentation attacks differ from injection attacks: what each one is, how each is detected, the separate standards that govern them, why a certification against one says nothing about the other, and where deepfakes fit into the picture. It is written for the fraud, risk, and engineering teams who need to make sure their verification stack actually covers both.
The one-line version is this. A presentation attack shows a fake to the camera. An injection attack skips the camera and feeds the fake straight into the software. Everything else follows from that difference.
- Presentation and injection attacks both defeat face verification, but through opposite routes: one in front of the camera, the other instead of it.
- A presentation attack shows a fake artifact to the sensor, a printed photo, screen replay, mask, or a deepfake on another device, which the camera genuinely captures.
- An injection attack bypasses the camera entirely, inserting a synthetic or pre-recorded video stream into the software pipeline, so the system never sees a real camera feed.
- Presentation attacks are caught by Presentation Attack Detection (PAD), standardized under ISO/IEC 30107-3, with iBeta certification.
- Injection attacks need a different defense, Injection Attack Detection (IAD), standardized under the newer CEN/TS 18099, with iBeta testing launched in 2026.
- The critical point: a system certified for PAD can have zero resilience to injection, because the two require fundamentally different technology.
- Injection is the fastest-growing attack vector of 2026, precisely because it bypasses the sensor-based defenses most systems rely on.
- A deepfake can arrive via either route, so a complete defense layers PAD, IAD, and deepfake detection, covering both how the fake enters and what it is.
The Core Difference: In Front of the Camera vs Instead of It
A useful way to hold the distinction is a border-crossing analogy. A presentation attack is a criminal approaching the border with a high-quality fake passport. All the security is focused on one point of interaction: an agent scrutinizes the physical document and the face presenting it. An injection attack is not a fake document at the desk at all; it is someone altering the border computer's records directly, bypassing the agent entirely. The first is a problem you solve by inspecting what is presented. The second is a problem at the data level, where nothing is presented to inspect.
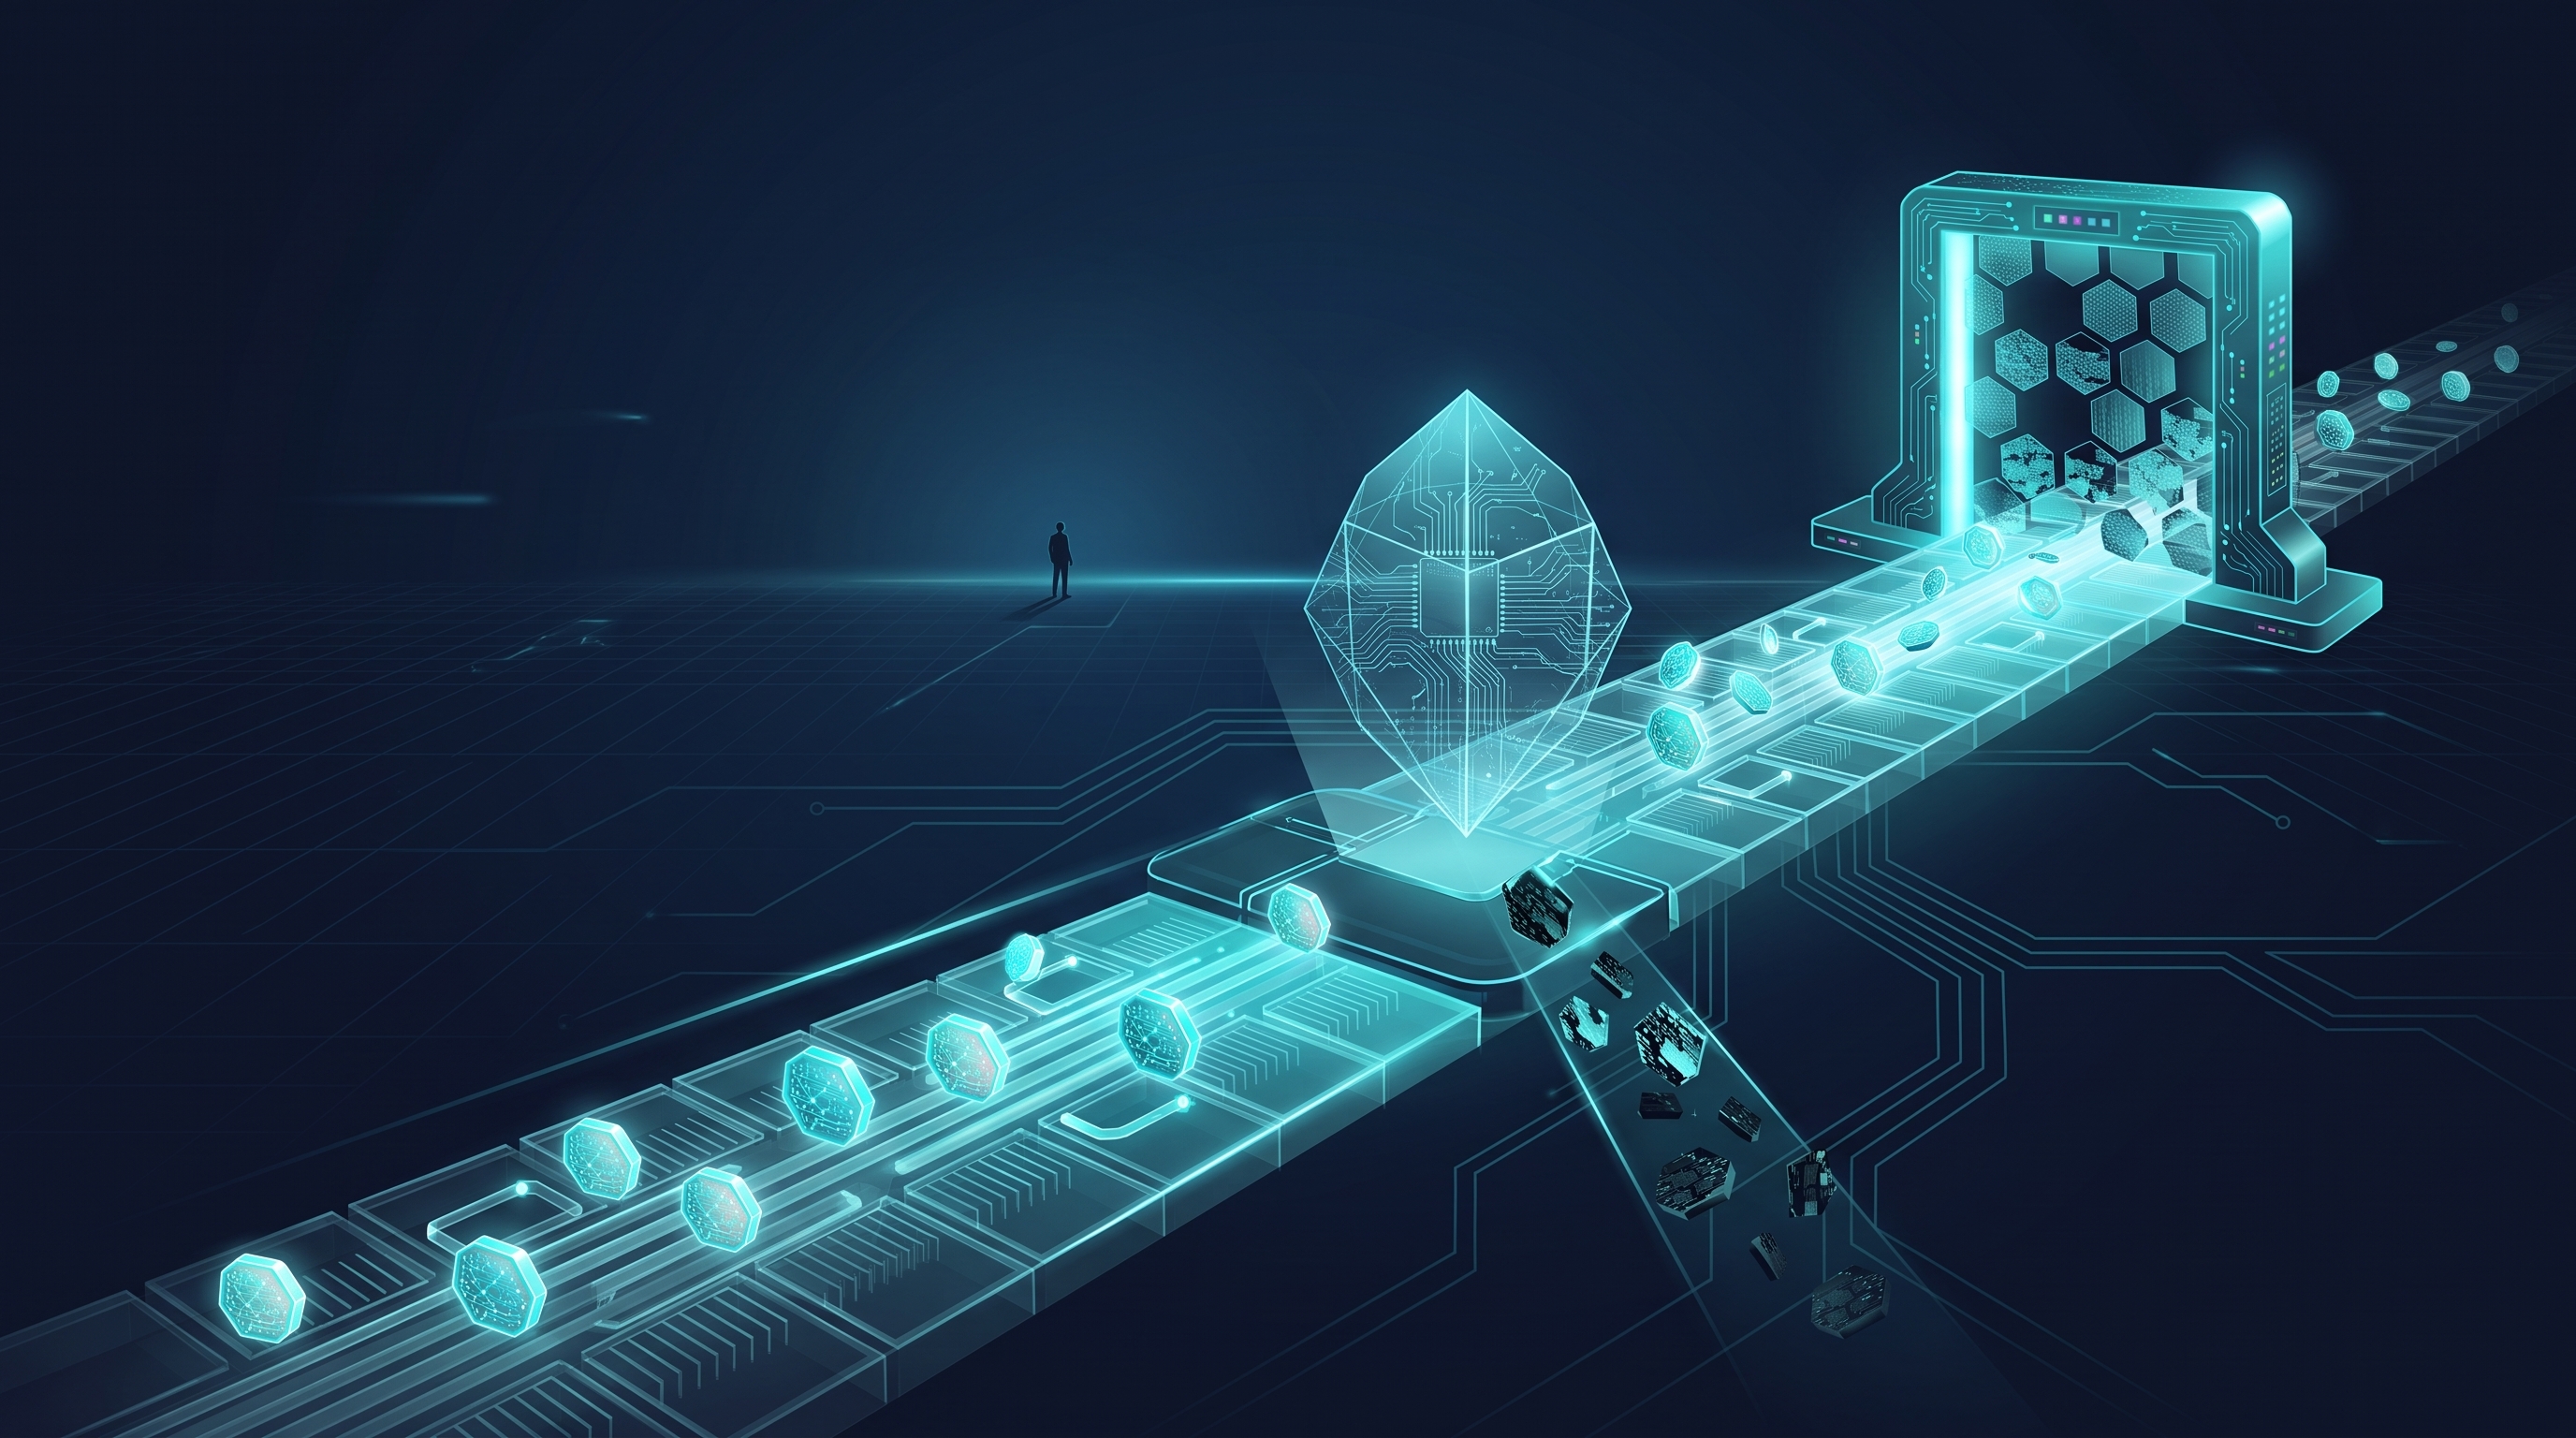
In technical terms, a presentation attack presents a fake artifact to the sensor, and the camera genuinely captures light bouncing off a physical object. An injection attack inserts fabricated data into the software pipeline between the capture device and the verification engine, so the biometric SDK or browser API never sees a real camera feed at all. One attack is in front of the lens; the other is instead of it. That single difference in where the fake enters determines everything about how each is detected.
What a Presentation Attack Is
A presentation attack is any attempt to spoof a biometric sensor by presenting a non-live artifact in front of it. The international standard ISO/IEC 30107-3 defines four canonical types, known as presentation attack instruments. A printed photo attack holds a photograph of the target, printed or shown on a screen, in front of the camera. A screen replay attack displays the target's face on a monitor, phone, or tablet. A pre-recorded video attack plays a video of the target back to the camera. And a 3D mask attack uses a physical mask shaped to resemble the target. A deepfake shown on a second device and held up to the camera also counts as a presentation attack, a "presented deepfake," because it still reaches the system through the lens.
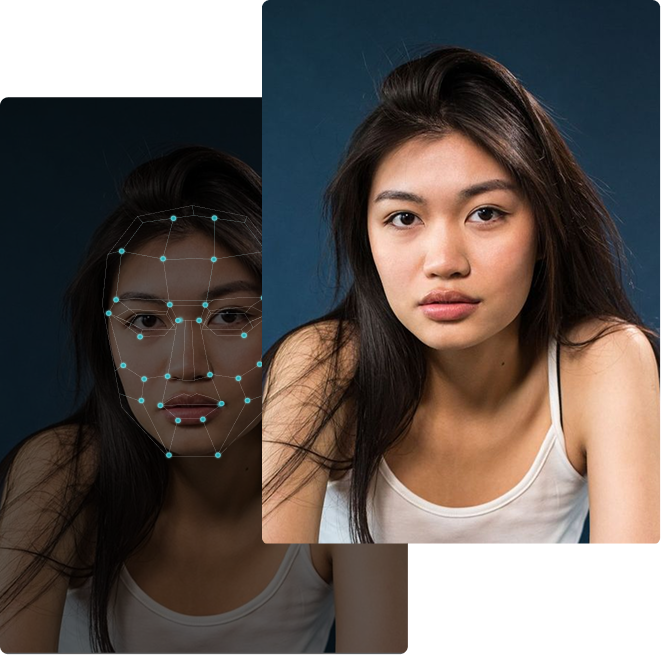
These are defended by Presentation Attack Detection, or PAD, the discipline ISO/IEC 30107-3 governs. PAD looks for the signs that what the camera sees is not a live person: the moiré patterns of a screen, the flat depth of a photo, unnatural reflections, or the absence of the micro-movements a real face makes. It is a mature field with well-established third-party testing, and certifications such as iBeta Level 1 and Level 2 provide independent validation that a system resists a defined set of presentation attacks. A PAD certificate is a real, earned credential, and it is the single most cited proof point in the biometric verification market.
What an Injection Attack Is
An injection attack does not interact with the camera at all. Instead of fooling the sensor, the attacker bypasses it and inserts a synthetic or pre-recorded video stream directly into the software capture layer. The most common method is virtual-camera software, which runs a face-swap or a saved video and exposes it to the operating system as though it were a webcam, so the verification app receives fabricated video believing it is a live feed. Other methods include emulator-driven attacks that run the app on a virtual device, hooks into the biometric SDK, interception of the video stream in transit, and direct manipulation of the verification API by submitting a crafted image or video. The chain is short and cheap: a face-swap model runs on consumer hardware, its output is routed into streaming software, and that output is presented to the system as a camera.
Because nothing is ever shown to a real lens, PAD does not address injection, and until recently there was no equivalent standard to test against. That changed with CEN/TS 18099, a European technical specification titled "Biometric data injection attack detection," approved in October 2024 and the first published document written specifically for this attack class. It characterizes injection attack instruments, gives detection guidance, and sets out test methodology and evaluation levels. In 2026, iBeta launched independent injection-attack-detection testing against it, up to Level 3, finally giving buyers third-party evidence rather than vendor claims, and a dedicated ISO standard, ISO/IEC 25456, is in development for expected publication in 2027. European regulators including ENISA, France's ANSSI, and Germany's BSI have all flagged injection as an emerging threat.
Why the Distinction Matters, and Where Deepfakes Fit
Here is the consequence that makes this more than terminology: the two attack vectors require fundamentally different testing and detection methodologies, and ISO/IEC 30107-3 was never designed to address injection. A vendor can hold PAD certification and still have zero resilience to injection attacks. In fact a system can hold the highest level of presentation-attack certification and have no defense whatsoever against a simple virtual camera. For years a PAD certificate became the default answer to an injection question, and buyers accepted it because the words look adjacent. They are not adjacent, and the gap is now the more urgent one, because injection has become the fastest-growing attack vector of 2026, precisely because it bypasses the sensor-based defenses most systems were built on. This threat is documented formally, including as a MITRE ATLAS case study of a live deepfake injected to evade mobile KYC.
Deepfakes sit across both categories rather than inside one, which is the last piece to get straight. A deepfake is not a third kind of attack alongside presentation and injection; it is content that can be delivered by either route. Shown on a phone to a camera, it is a presented deepfake that PAD may catch. Fed through a virtual camera, it is an injection attack that PAD will miss. So presentation versus injection describes how the fake enters, while deepfake describes what the fake is. A complete defense therefore has to answer three separate questions, and no single certification covers all of them.
How to Defend Against Both
The practical implication is that a verification stack has to cover both the camera-facing and the pipeline-facing attack surfaces, plus the synthetic content itself, and a face-verification solution built only on liveness certification leaves the injection pathway wide open. That means three layers working together. Presentation Attack Detection handles the artifacts shown to the camera. Injection Attack Detection, using device and session-integrity checks that surface virtual cameras and emulators and confirm the feed comes from real hardware, handles the pipeline. And deepfake detection analyzes the media itself for synthetic signatures, catching a face swap or AI face however it was delivered. When evaluating any of these, the right move is to ask for independent evidence, an ISO/IEC 30107-3 certificate for PAD, a CEN/TS 18099 evaluation for IAD, and real-world validation for deepfake detection, rather than accepting one certificate as proof of all three.
This is where DuckDuckGoose, based in Delft, focuses within that stack. DeepDetector provides the deepfake-detection layer, analyzing images and video for the signatures of synthetic media regardless of whether a fake arrived as a presented deepfake or an injected stream, with explainable output and ISO 27001, SOC 2, and GDPR compliance. It complements, rather than replaces, the presentation and injection detection a complete system also needs. For the injection vector in depth, see our guide to how injection attacks feed deepfakes into verification, and for why the liveness layer alone is not enough, why liveness checks fail against deepfakes.
Frequently Asked Questions
What is the difference between a presentation attack and an injection attack?
A presentation attack shows a fake artifact to the camera, such as a printed photo, a screen replay, a mask, or a deepfake on another device, which the camera genuinely captures. An injection attack bypasses the camera entirely and inserts a synthetic video stream directly into the software pipeline, so the system never sees a real camera feed. The difference is where the fake enters: in front of the camera versus instead of it.
What are examples of each?
Presentation attacks include printed photos, faces shown on a phone or monitor, pre-recorded video played to the camera, and 3D masks. Injection attacks include virtual-camera software feeding a synthetic stream, emulator-driven attacks, hooks into the biometric SDK, interception of the video stream, and direct manipulation of the verification API.
How is each attack detected?
Presentation attacks are caught by Presentation Attack Detection (PAD), which looks for signs that the camera is not seeing a live person, governed by ISO/IEC 30107-3 and validated by iBeta certification. Injection attacks need Injection Attack Detection (IAD), which uses device and session-integrity checks to confirm the feed comes from a real camera, governed by the newer CEN/TS 18099 specification.
Does a PAD certificate mean a system stops injection attacks?
No. This is the most important point. PAD certification under ISO/IEC 30107-3 tests only presentation attacks, and a vendor can hold even the highest PAD level while having no defense against a virtual camera. The two vectors require fundamentally different technology, so an injection question needs a CEN/TS 18099 evaluation, not a PAD certificate.
Are deepfakes a presentation attack or an injection attack?
Either. A deepfake is content, not a delivery method. Shown on a device to the camera it is a presented deepfake, which PAD may catch; fed through a virtual camera it is an injection attack, which PAD will miss. That is why deepfake detection is a separate layer from PAD and IAD, answering what the fake is rather than how it entered.
Which is more common now?
Presentation attacks remain common at scale, but injection is the fastest-growing vector of 2026, because accessible deepfake tools and off-the-shelf virtual-camera software make it easy, and because it bypasses the sensor-based defenses most systems were built around. Both are active, so both must be addressed.
What do I need to defend against both?
Three layers: PAD for artifacts shown to the camera, IAD for the pipeline, and deepfake detection for the synthetic content itself. Ask for independent evidence for each, an ISO/IEC 30107-3 certificate for PAD, a CEN/TS 18099 evaluation for IAD, and real-world validation for deepfake detection, rather than treating one certificate as proof of all three.
About the author